Is Threat Intelligence in Your 2027 Cyber Security Budget?
Most UK organisations will sign off their April budgets in the next few weeks, and most of that money goes on tools that help them respond to incidents. This post makes the case for also funding intelligence that tells you what’s coming. It explains why more data doesn’t mean more intelligence and sets out three questions good intelligence should answer. It also gives five questions to check your current approach before the budget closes. Customers, including a global pharmaceutical company and a top-four UK bank, describe getting earlier warning, better prioritisation and fewer alerts.

Before you sign off your cyber security budget, is intelligence on your list?
Budgets for the year ahead are being finalised now. For many UK organisations, the spend that starts in April will be signed off in the next few weeks.
Most of that money will go on tools that help you respond when something happens. Before you sign, ask whether you are also investing in the intelligence that tells you what is coming.
The difference is measurable. A CISO at a global pharmaceutical company told us their team is now typically 12–36 hours ahead on reports and key findings. In security, that is the gap between preparing and reacting.
More data isn’t more intelligence
Security teams are not short of information. They are short of time to work out which of it matters. Threats evolve constantly and threat actors adapt quickly. Meanwhile, feeds, alerts and reports keep arriving. Every alert that has not been validated costs analyst hours spent filtering and checking instead of acting.
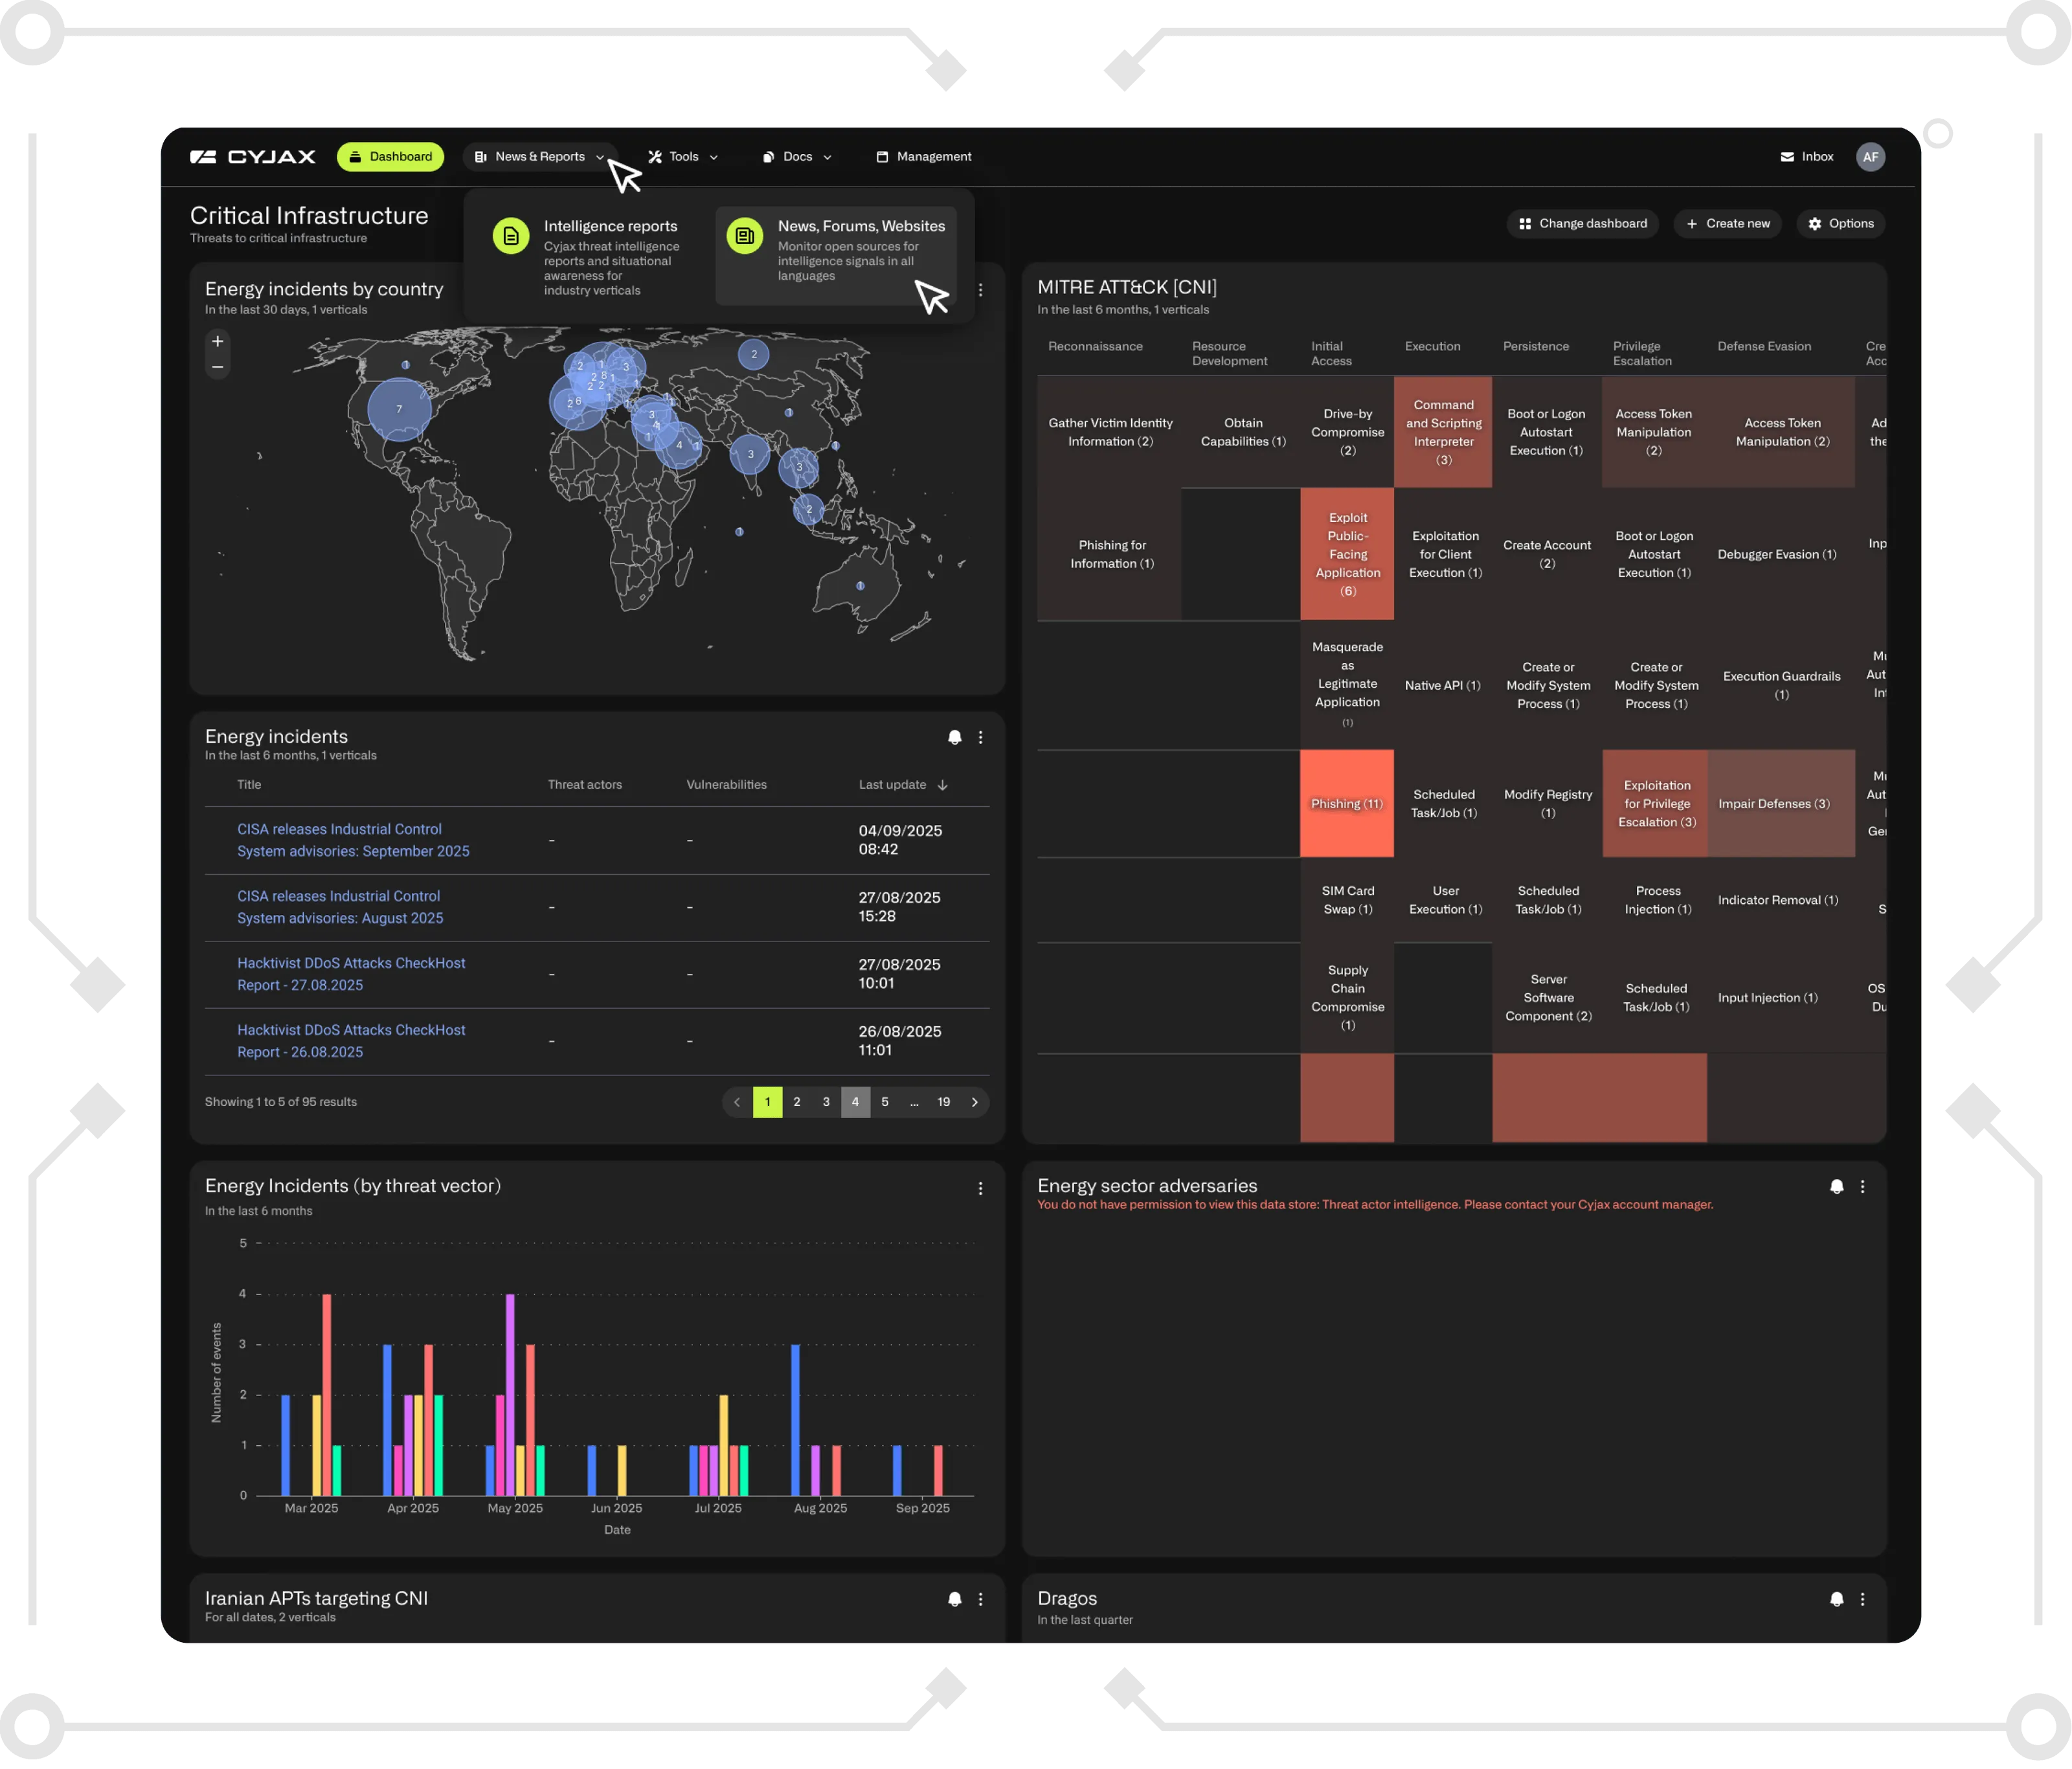
Good intelligence reverses that. It is collected widely, validated, enriched with expert context and prioritised, so what reaches your team is already relevant.
Three questions good intelligence answers
Any intelligence investment should answer three questions for your organisation:
- What threats are emerging?
- Which of them matter to us?
- What should we do about them?
If your intelligence stops at the first question, it is just more data. The value lies in the second and third.
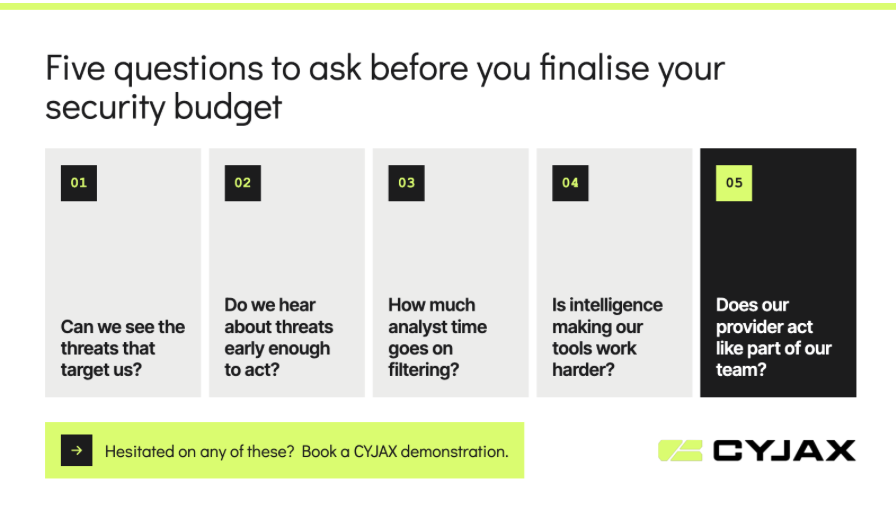
Five questions to ask before you finalise your budget
Use these as an honest check on your current approach, whoever provides your intelligence today.
- Can we see the threats that target us specifically? Across the open, deep and dark web, including our brand, people and supply chain.
- Do we hear about emerging threats early enough to act? Or do we learn about them from the news, or from an incident?
- How much analyst time goes on filtering rather than acting? Noise is a cost. Validated, prioritised intelligence gives that time back.
- Is intelligence making our existing tools work harder? Better context means sharper triage, investigation and control tuning.
- Does our provider act like part of our team? Access to analysts, tailored reporting and responsive support when it counts.
If any of these gave you pause, address it while the budget is still open, not after an incident exposes the gap.
What our customers see
The best evidence for an intelligence investment comes from the teams already using it.
Earlier warning.
“CYJAX added depth to the broad coverage we already have. We are now able to take quicker and more informed actions as CYJAX is typically 12–36 hours ahead on reports and key findings.” — CISO, global pharmaceutical company
Spend directed where it counts.
“CYJAX enabled us to identify which threats were most relevant, helping our team prioritise threats and increasing the efficiency of our security spending.” — Head of Threat Intelligence, top-four UK bank
Less noise, better controls.
“CYJAX provided the additional context and filtering we needed to rapidly triage and qualify which alerts need actioning. This freed our team up to make adjustments to our security controls, vastly reducing the number of alerts coming in.” — CTO, UK Power Networks
That is the test when budgets are under scrutiny: intelligence should make every other line of spend work harder, not just add another one.
Why CYJAX belongs on your shortlist
CYJAX is a UK-based threat intelligence company. For 14 years we have combined a purpose-built platform with specialist analysts to give security teams clear, actionable intelligence on the threats that matter to them.
- Analyst-enriched intelligence: every finding validated and given context by people who know the threat landscape.
- Broad visibility: open, deep and dark web sources, Telegram, technical feeds and geopolitical monitoring, watched 24/7.
- Tailored to you: alerts, threat profiles and reporting aligned to your sector, risk appetite and priorities.
- Fits your stack: delivered through the platform, email and API, with 10+ native integrations.
- Independently certified: ISO 27001:2022 certified for information security management.
- A partner that stays: named analyst support and regular reviews.
- Cost-effective: a mature intelligence capability without the cost of building one in-house.
Make intelligence part of the conversation now
The decisions made in this budget cycle will shape the capabilities your team relies on all next year. Intelligence should be part of that conversation from the start, not something prioritised after an incident.
Start with the five questions above. Download the checklist and take it into your next budget meeting. If it highlights a gap, our team will show you what CYJAX would surface for your organisation.
Recommended for you
Get Started with CYJAX CTI
Empower Your Team. Strengthen Your Defences.CYJAX gives you the intelligence advantage: clear, validated insights that let your team act fast without being buried in noise.