Cineworld Glitch Purportedly Allows Users To See Member Card Details
On 17 September 2026, users on X (formerly Twitter) posted that payment details belonging to other individuals had appeared on the Cineworld app under their personal accounts.

On 17 September 2026, users on X (formerly Twitter) posted that payment details belonging to other individuals had appeared on the Cineworld app under their personal accounts. The UK-based cinema chain had rolled out a new app and website update just two days previously, with Cineworld Unlimited members appearing to be particularly affected by this issue. Cineworld Unlimited is a scheme which allows users to watch unlimited films and receive exclusive discounts and member rewards. One of the most viewed threads regarding this can be seen in the figures below.
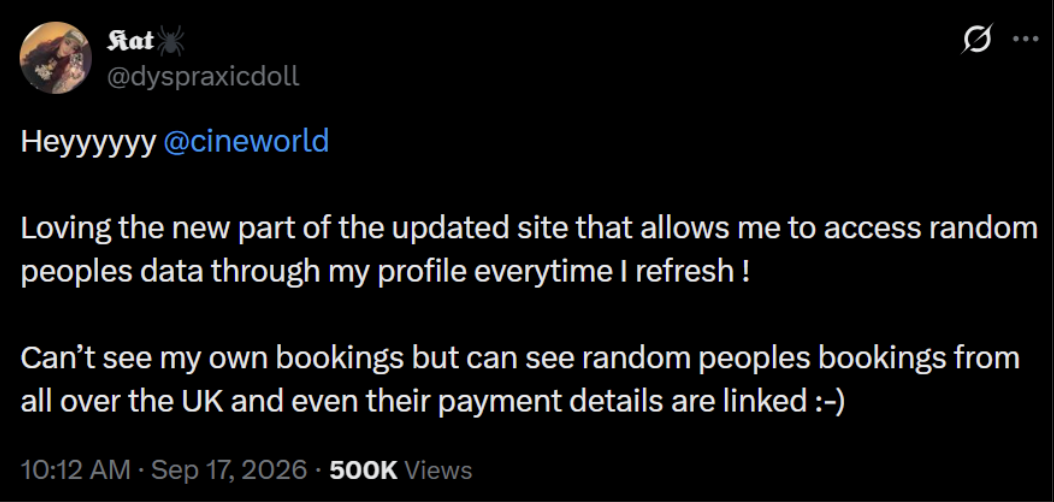
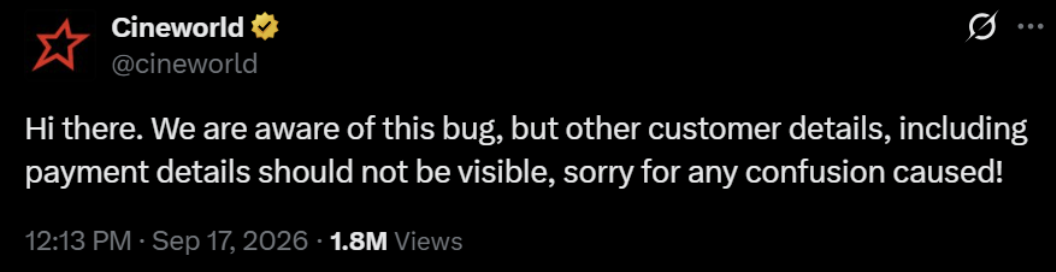
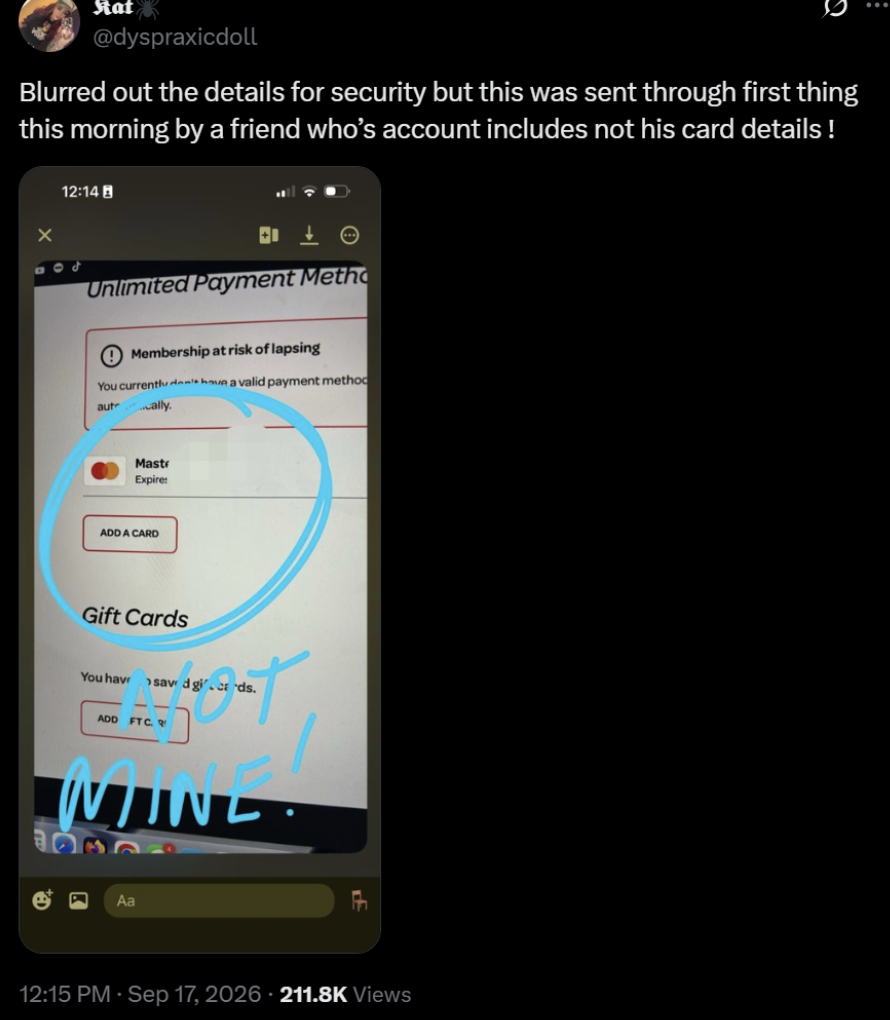
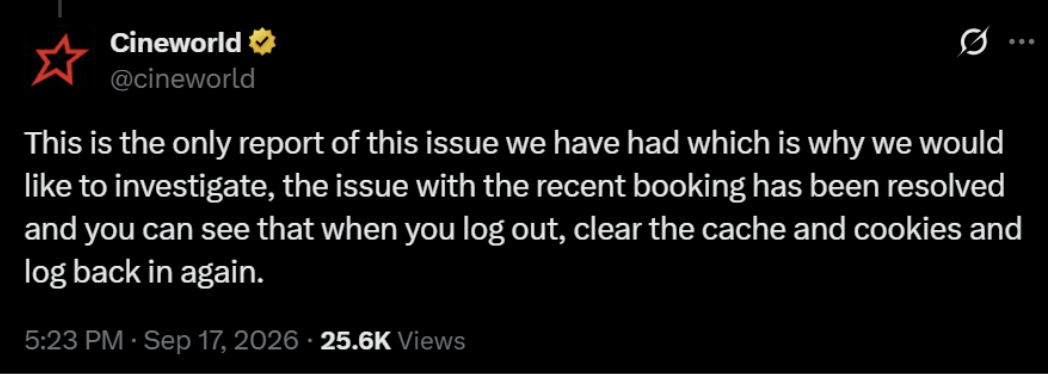
Despite the cinema chain stating that dyspraxicdoll was the only user to report this issue, multiple posts on X showed that other users also had problems with random card details and transactions appearing in their accounts. These are shown in the figures below.
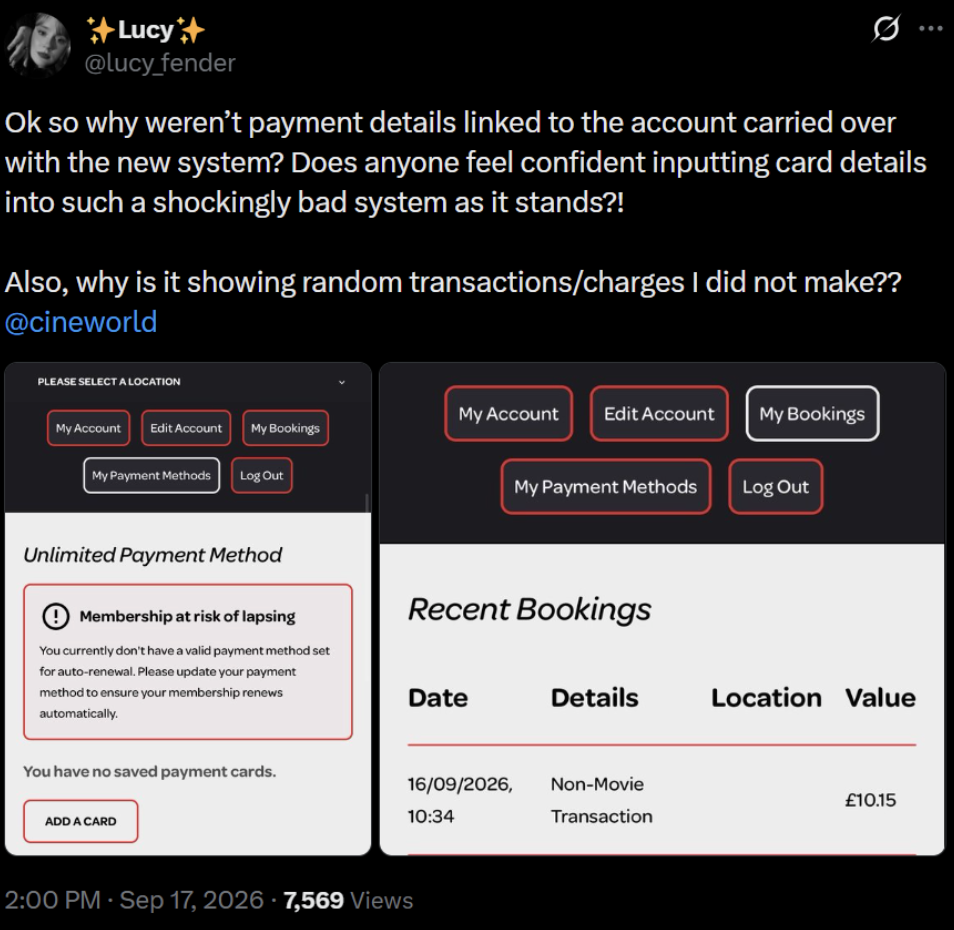
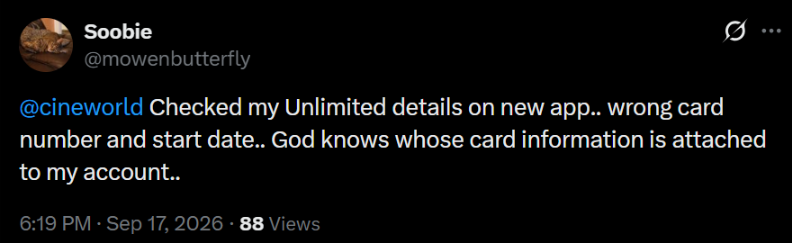
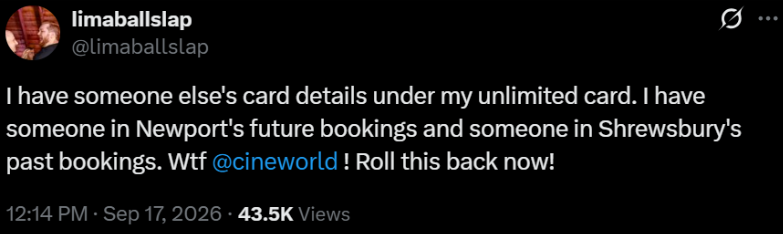
These posts highlight how the issue appears to be more widespread than Cineworld previously stated in its first response. This is further evidenced as users on other social media platforms such as Reddit also appear to be experiencing the same issue.
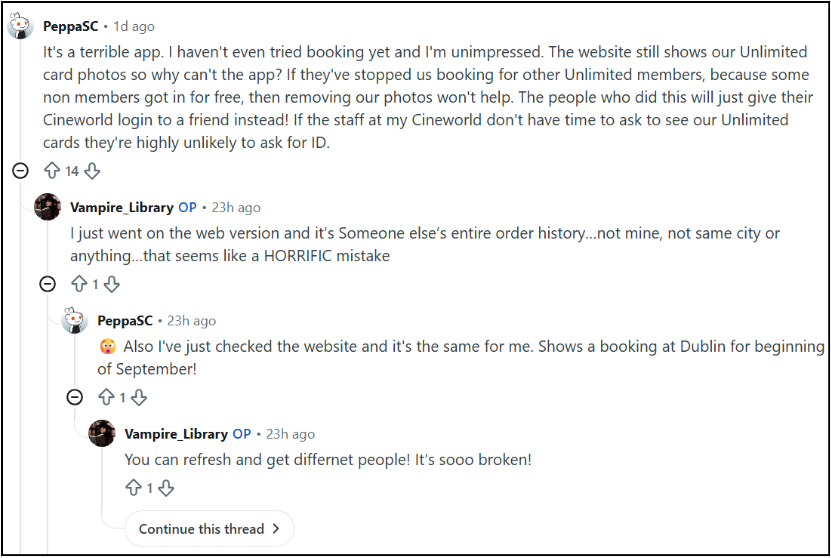
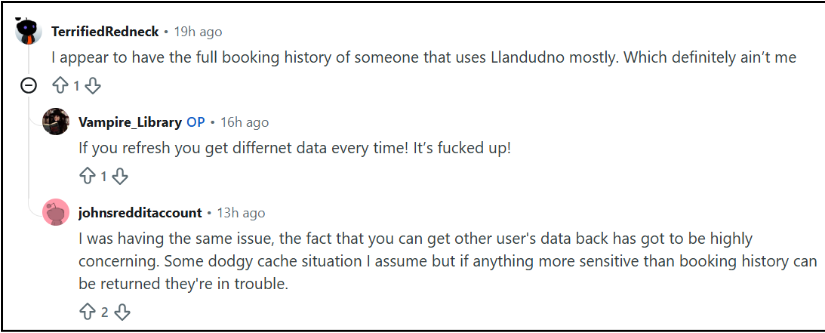
As users can allegedly see card details that do not belong to them, this could constitute the unauthorised exposure of personally identifiable information (PII) and financial data under UK GDPR. Under this legislation, organisations have 72 hours to report a breach to the ICO or face a fine of up to £8.7 million or 4% of global turnover. Whilst Cineworld has stated that the issue is just a glitch, this may still constitute a failure of security. This is because Article 32 of GDPR states that companies must use technical and organisational measures to ensure that data is kept secure. As such, the reported glitch means that users purportedly being able to see random card details is a failure of this and may be classed as an unauthorised personal data breach. Additionally, this may also constitute a failure to comply with the Payment Card Industry Data Security Standard (PCI DSS), a global security framework which ensures that organisations safely accept, process, store, and transmit card data. This framework is managed by the PCI Security Standards Council and applies to all organisations which handle debit or credit cards. If an organisation fails to comply with PCI DSS, it effectively breaches its merchant agreement contract with its payment processor or acquiring bank. This can lead to monthly fines for non-compliance and further financial penalties if card details end up being stolen. Scheme fines can then be passed down and the ICO can also act if customer personal data was exposed under UK law.
There is currently no evidence of this alleged information being misused; however, fraudsters and cybercriminals are known to use stolen card details to conduct malicious activity. This may include making fraudulent online purchases or placing names, numbers, and CVVs into bundles to be sold on cybercriminal marketplaces. Cybercriminals which are financially motivated often use stolen card details to make a profit, making them a lucrative asset to those operating across the landscape. At the time of writing, there has been no observed threat actor discussion regarding this potential leak.
More broadly, this issue will likely cause reputational damage to Cineworld. The app and website appear to have been developed within the UK, with Cineworld plc and digital development agency Can Factory being responsible for managing and publishing the service. What this incident highlights is a lack of safeguarding in the app update, which could potentially lead to financial harm if a user were to attempt to misuse the allegedly exposed details. In addition to this, users on Reddit have been observed negatively commenting on the app update, as shown in the figure below.
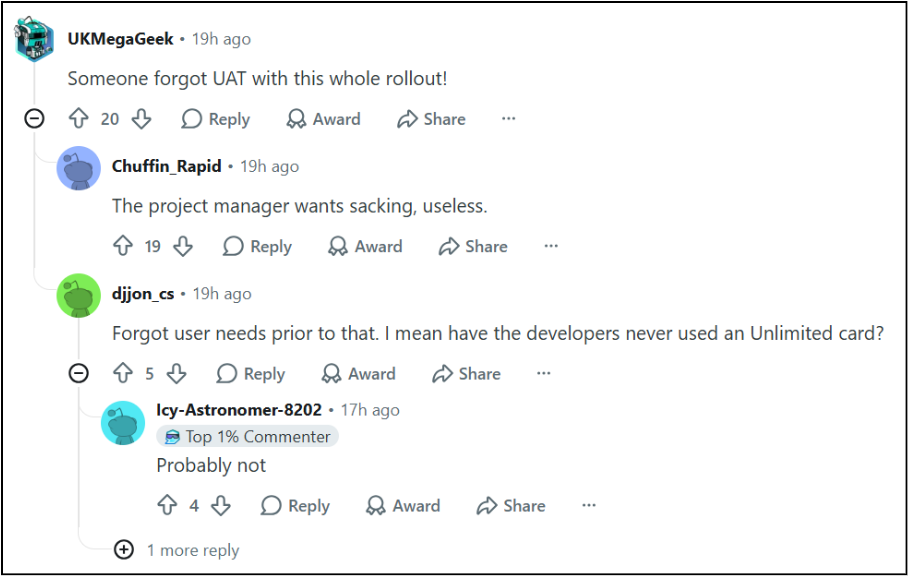
The mention of UAT is in reference to user acceptance testing, which is the final phase of software development where actual users test an application to see if it meets business requirements and operates as expected. As such, the unintentional exposure of card details combined with a lack of user satisfaction with the app update itself will likely increase the reputational damage caused. This negative rhetoric is likely to continue if Cineworld is deemed to not have adequately addressed user concerns regarding these issues.
Recommended for you
Get Started with CYJAX CTI
Empower Your Team. Strengthen Your Defences.CYJAX gives you the intelligence advantage: clear, validated insights that let your team act fast without being buried in noise.