Why MSSPs Need Threat Intelligence That Goes Beyond a Feed
MSSPs are being asked to secure more clients, across more industries, with more tools than ever before. This post explains why simply adding another threat feed to the stack doesn't solve the problem, and what MSSPs need to operationalise intelligence at scale.
Key takeaways
- MSSPs don't need more threat data: they need intelligence that's already contextualised and validated.
- Generic feeds add noise. The average organisation already receives nearly 3,000 alerts a day, with 63% going unaddressed.
- One-size-fits-all intelligence ignores the fact that every client has a different sector, risk profile, and threat exposure.
- Contextualised, pre-validated intelligence removes manual triage work from analysts, cutting time spent chasing false positives.
- Operationalised intelligence lets MSSPs scale service quality across a growing client book without scaling headcount at the same rate.
Managed Security Service Providers sit at an unusual point of pressure in the cybersecurity ecosystem. A single MSSP might be responsible for defending a logistics firm, a regional law practice, and a manufacturing group at the same time, each with a different risk profile, a different attack surface, and a different tolerance for disruption. Multiply that across a full client book and the operational challenge becomes clear: MSSPs are not securing one environment; they are securing dozens simultaneously, often with a team that has not grown at the same rate as the client list.
Adding another data source into that mix rarely helps. What MSSPs need is not more information. It is intelligence they can put to work across every client they serve.
The challenge of managing multiple client environments
Every client an MSSP onboards brings its own technology stack, its own third-party dependencies, and its own threat exposure. A retail client cares about card skimming and loyalty fraud. A healthcare client cares about data exfiltration and ransomware against clinical systems. A logistics client cares about supply chain compromise. Analysts are expected to hold all of this context in their heads while triaging alerts in real time, and the cost of getting it wrong is measured in client trust.
This is compounded by tooling. Blumira's 2025 survey of managed service providers found that more than 75% of MSPs experienced alert fatigue at least monthly, with tool sprawl, false positives, and weak integrations contributing to delayed responses. When each client relationship effectively runs its own detection stack, the SOC is not managing one environment with edge cases. It is managing dozens of environments with almost nothing standardised between them.
Why more threat data creates more noise
The instinctive response to "we're missing threats" is often to buy another feed. In practice, this usually makes the underlying problem worse rather than better. Organisations now receive an average of 2,992 security alerts every day, and 63% of them go unaddressed entirely, according to Vectra AI's 2026 State of Threat Detection and Response research. That daily average has fallen from 3,832 the year before, yet the share going unaddressed has barely moved. More filtering has not produced more relevance.
For an MSSP, that noise problem doesn't stay contained to one client. It multiplies across the whole portfolio. A feed that adds volume without adding relevance simply pushes more raw material into an already overloaded triage queue, and the analysts closest to the client relationship are the ones who absorb the cost.
Why generic intelligence doesn't work for every client
Even when a feed is well-curated, it is usually built for a general audience rather than any one organisation. A generic indicator list treats a university and an energy supplier as equivalent consumers of the same intelligence, when their adversaries, their regulatory obligations, and their acceptable risk thresholds have almost nothing in common.
This mismatch shows up most clearly at the client level. A generic feed flagging a credential-stuffing campaign against retail loyalty schemes is high-priority intelligence for one client on an MSSP's books and noise for the other twenty. The same feed will rarely carry the detail that matters to the healthcare supplier two accounts over, because narrowing to that specificity is exactly what a general-audience feed cannot do. Someone still has to make that relevance judgement, and in a generic model that someone is the analyst. DSIT research on cyber security skills in the UK labour market finds that 49% of UK businesses have a basic technical cyber skills gap, covering tasks as fundamental as configuring firewalls and detecting malware, which is precisely the capability an MSSP is being paid to provide. A one-size-fits-all feed asks the client, or the MSSP's own analysts, to do the contextualisation work that intelligence should already have done for them.
The importance of contextualised and validated intelligence
Contextualised intelligence answers the questions a generic feed leaves open. Is this indicator relevant to this client's sector? Has it been independently validated, or is it an unconfirmed report circulating in open sources? What is the actual likelihood of impact given this client's exposure, and what should the analyst do about it in the next fifteen minutes?
This distinction is measurable. Microsoft and Omdia's State of the SOC 2026 research found that 46% of all alerts prove to be false positives, meaning close to half of an analyst's daily workload produces zero security value. Validated, human-analysed intelligence exists specifically to close that gap, filtering out noise before it ever reaches the analyst rather than asking them to filter it themselves under time pressure. For an MSSP working across multiple sectors, that validation step must happen once, centrally, and then be applied consistently to every relevant client, not repeated from scratch by each account team.
How MSSPs can turn intelligence into a scalable service
The MSSPs that scale successfully are the ones that treat threat intelligence as an operational layer, not a data subscription. That means intelligence tagged and segmented by sector, so a healthcare client only sees what matters to healthcare. It means validated reporting that analysts can act on directly, without spending time re-verifying source credibility. It means multi-tenancy that holds up commercially, with intelligence separated cleanly per client and client-ready reporting the MSSP can put its own brand on. And it means intelligence that plugs into existing SIEM, SOAR, and ticketing workflows, so contextualisation happens automatically rather than manually for every client, every time.
Done well, this turns threat intelligence from a cost centre into a service differentiator. MSSPs can offer genuinely tailored protection across a diverse client book without linearly scaling headcount, which matters given that 95% of UK cyber professionals report at least one skills gap in their own organisation, with 58% describing their shortages as critical or significant, according to ISC2 research published in May 2026. Intelligence that is already contextualised and validated is one of the few ways to offset that shortage rather than be limited by it.
What this looks like with CYJAX
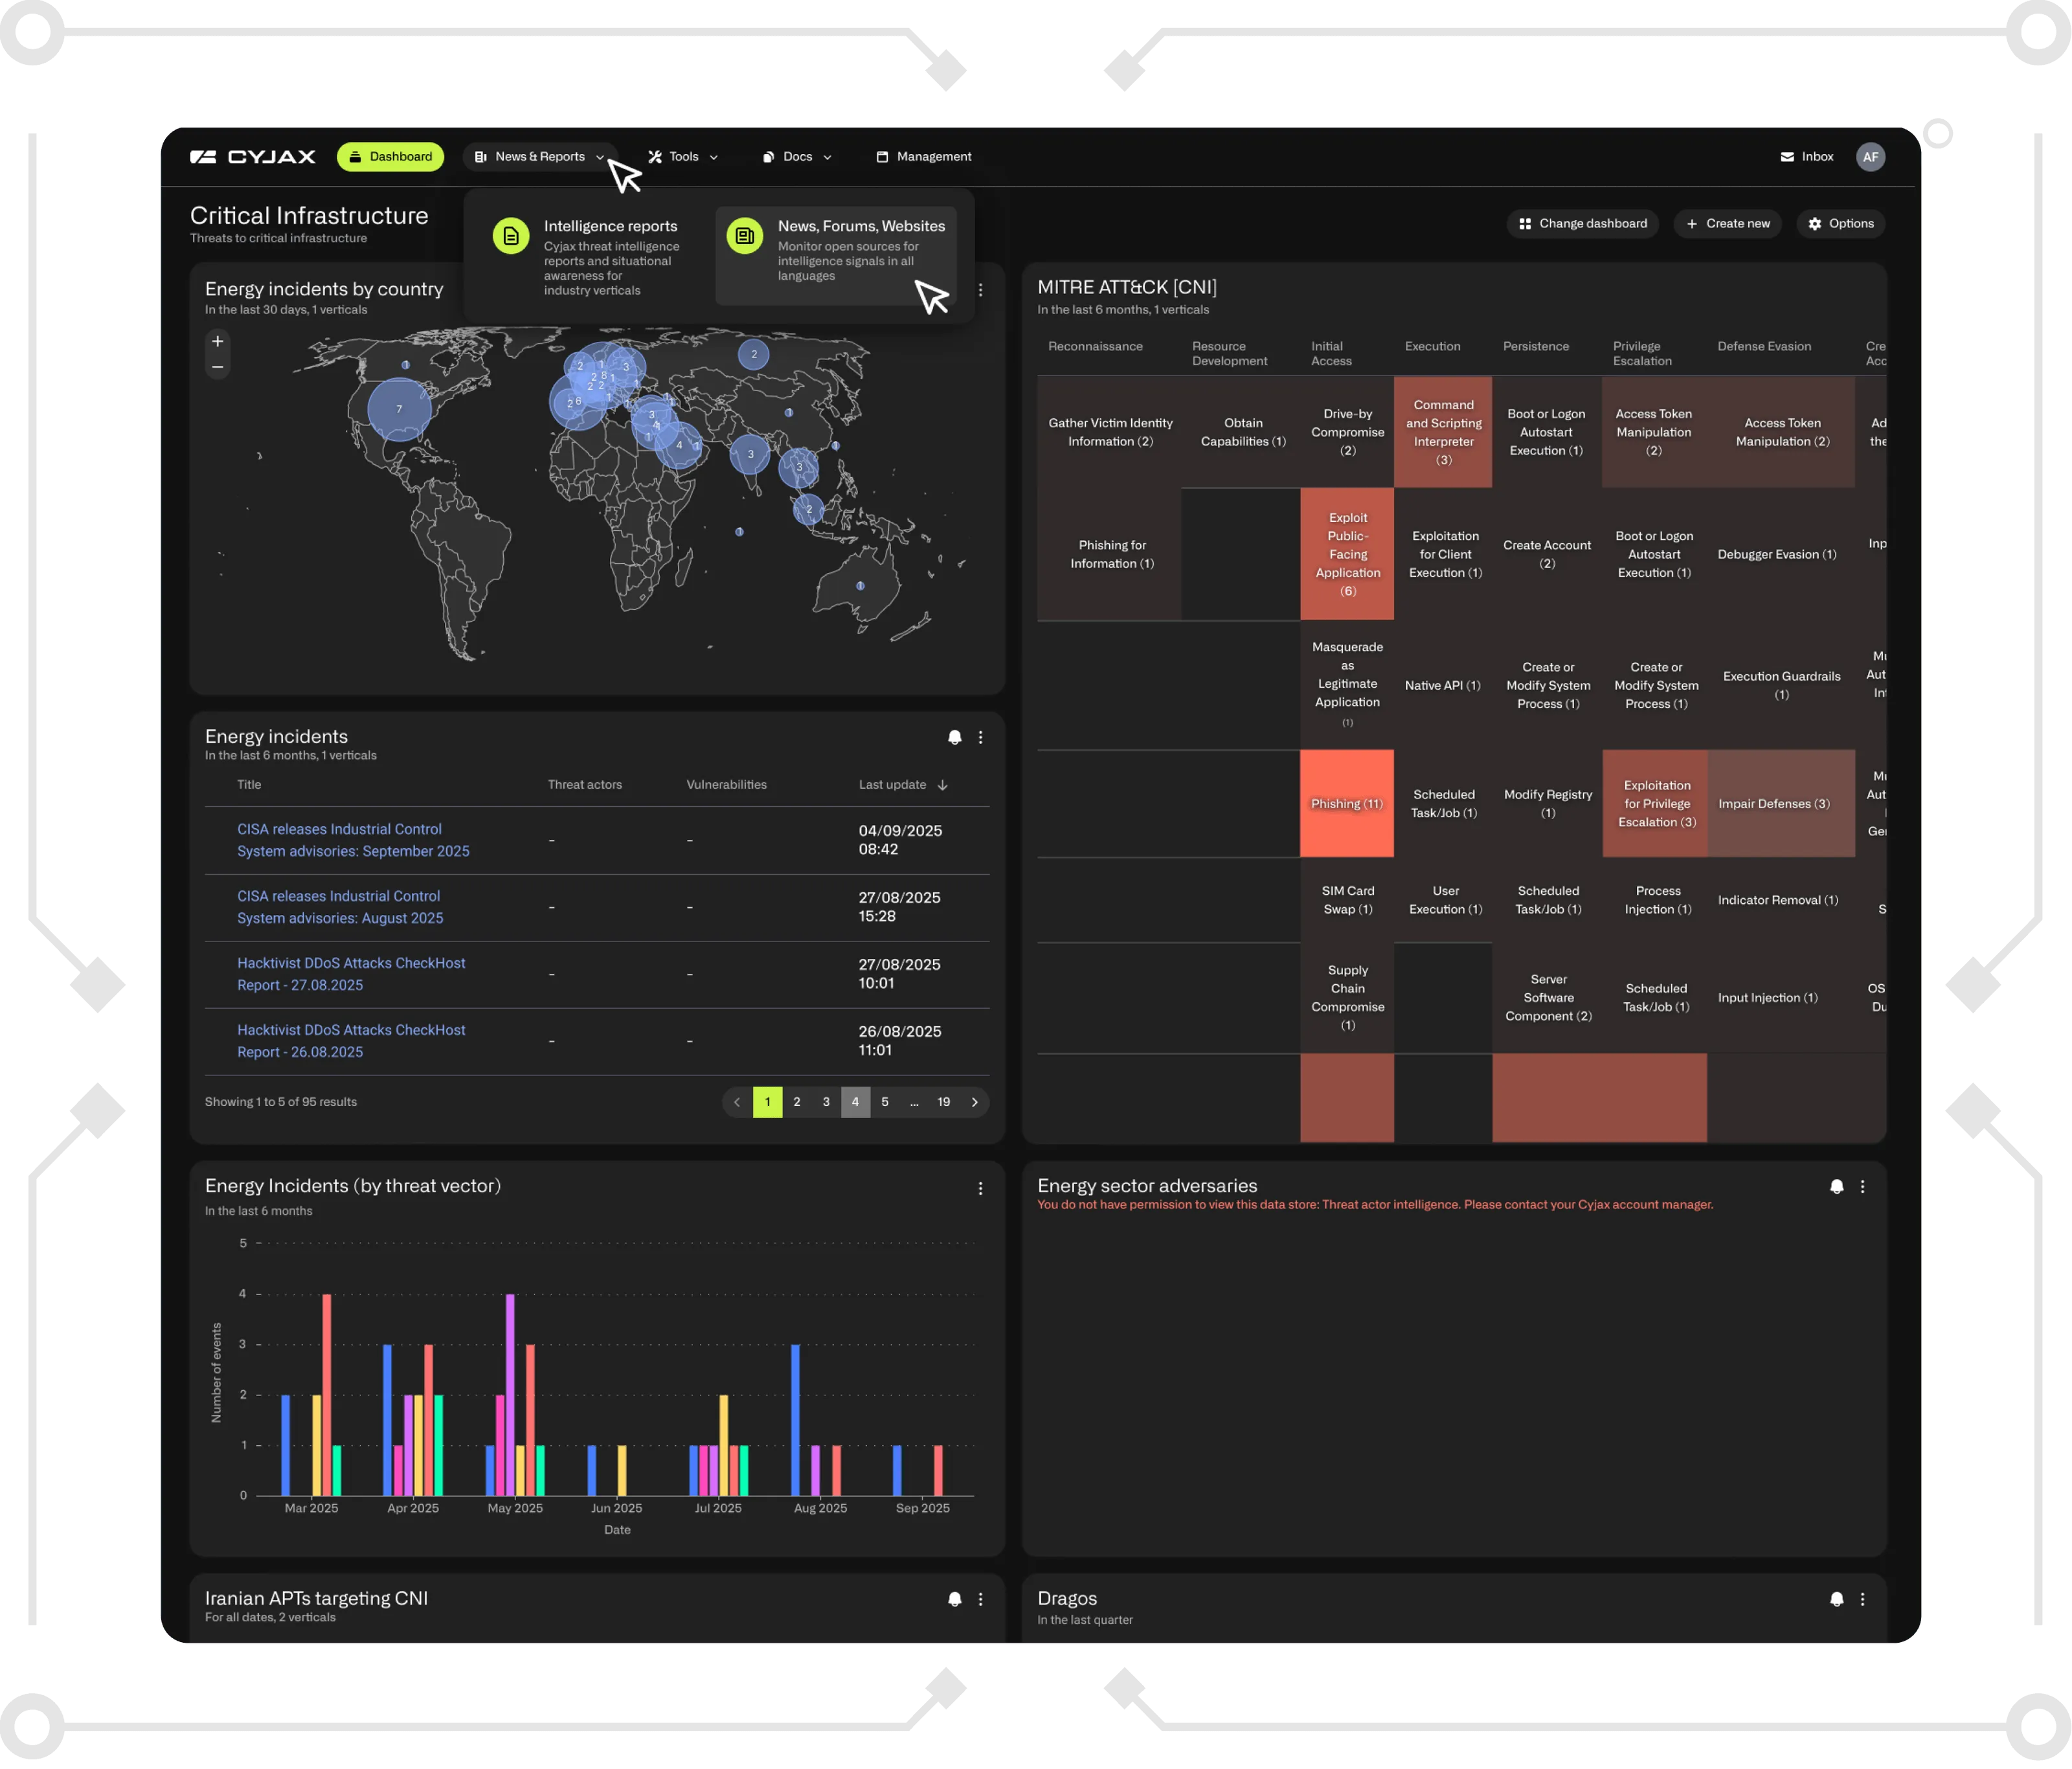
CYJAX operates as a trusted extension of your team, with intelligence validated by analysts before it reaches yours. For an MSSP, that means the contextualisation work happens once, centrally, and is then applied to every client that needs it, rather than being repeated by each account team under time pressure. Sector tagging, validated reporting and integration into existing SIEM, SOAR and ticketing workflows are what turn an intelligence subscription into a service you can sell. See our Domain Monitor and sector landing pages for how this is packaged for partners.
Recommended for you
Get Started with CYJAX CTI
Empower Your Team. Strengthen Your Defences.CYJAX gives you the intelligence advantage: clear, validated insights that let your team act fast without being buried in noise.